
Cloud-delivered Firewall Management Center
Introduction to Cisco's latest offering for managing Cisco Secure Firewall.
Language: English | 日本語
Introduction
Cisco Defense Orchestrator (CDO) is now Firewall Management in Security Cloud Control (SCC). Older screenshots and glossary entries in this article retain the CDO name.
The cloud-delivered Firewall Management Center(cdFMC) brings the management capabilities of the Firewall Management Center (FMC) within Cisco Defense Orchestrator (CDO). Adoption is made easier with a minimal learning curve, as we have retained the FMC's policy management workflows and user experience. Also, the built-in migration wizard enables easy migration from privately managed FMCs (Hardware appliance, private or public cloud) to the cloud-delivered FMC.
Cloud-delivered FMC is available through Cisco Defense Orchestrator, a SaaS-delivered offering, so Cisco manages the upkeep of the service, eliminating the OpEx associated with maintaining a virtual or hardware management appliance.
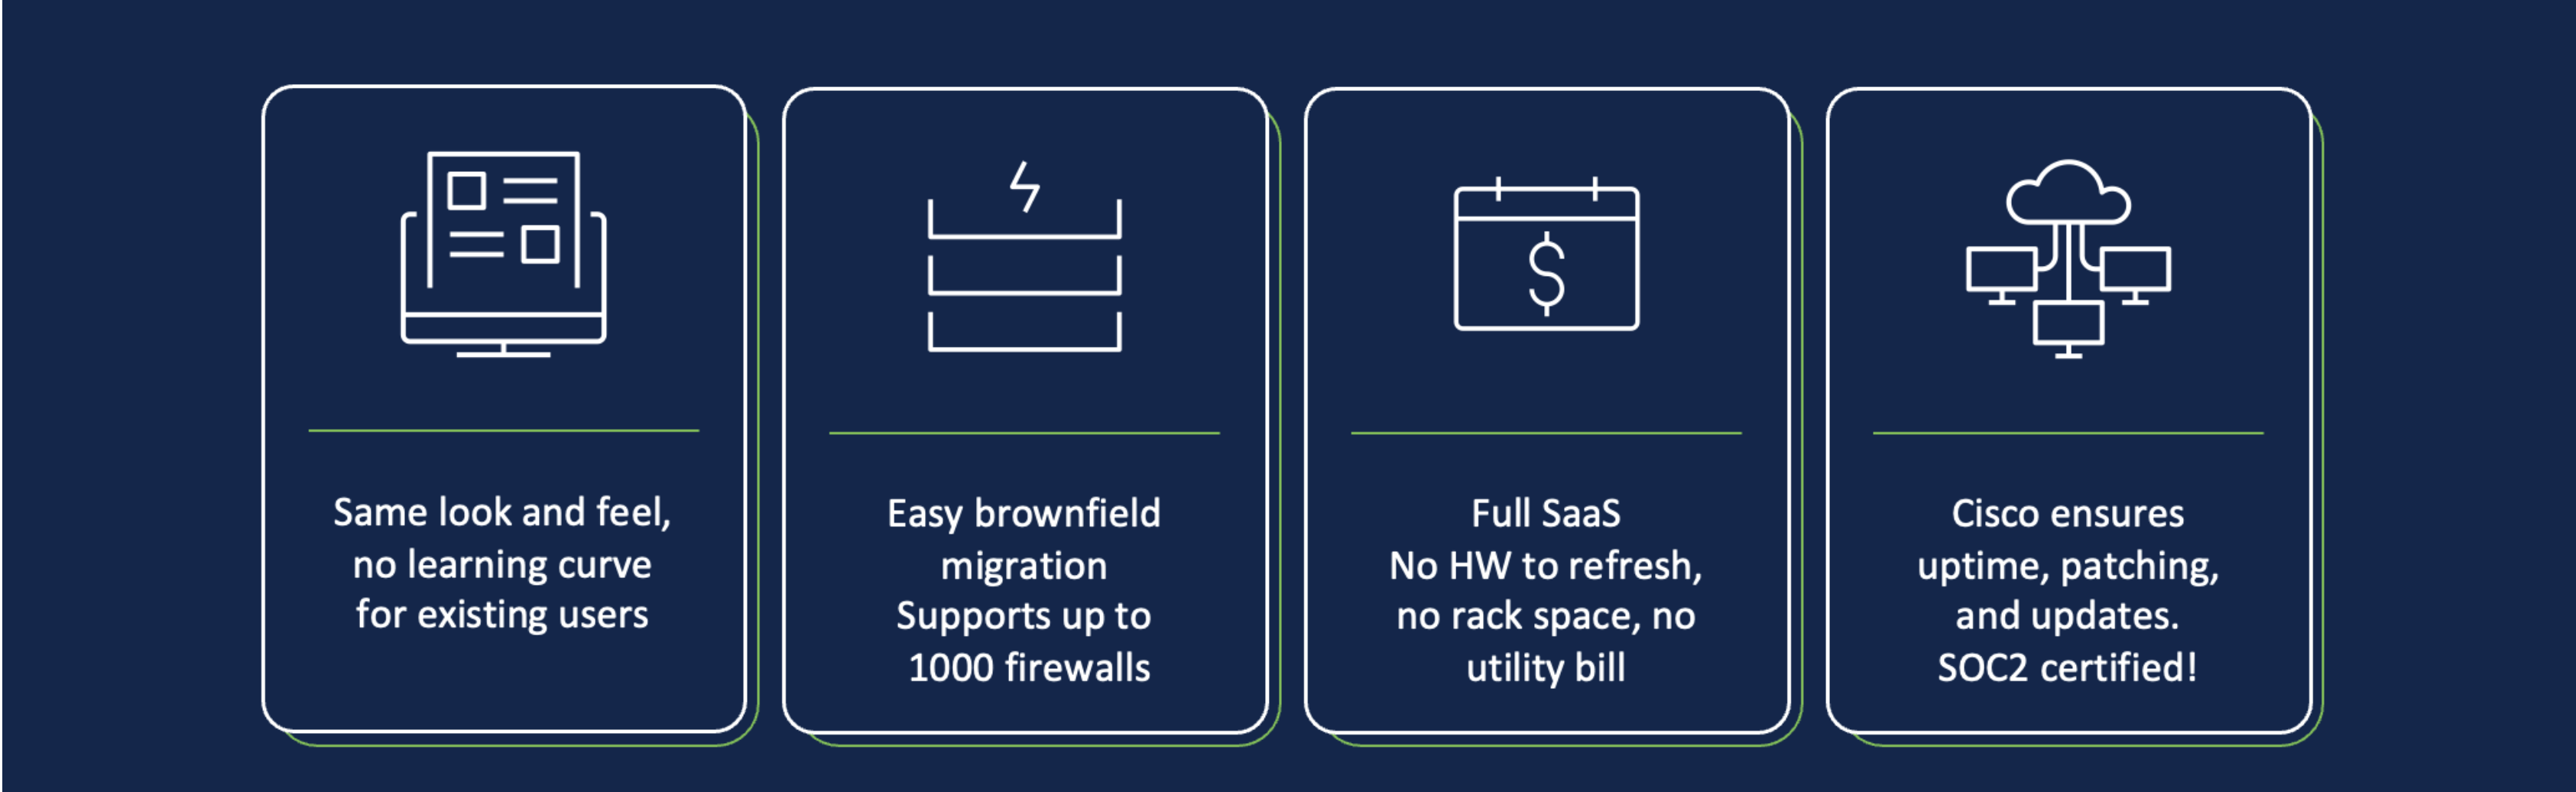
Benefits of cloud-delivered Firewall Management Center
Cloud-delivered FMC manages supported Secure Firewall Threat Defense hardware and virtual deployments. Confirm platform and software-version support in the current cloud-delivered FMC compatibility and onboarding documentation before deployment.
Key Benefits
Familiar User Experience
The cloud-delivered FMC reuses most of the policy configuration components to minimize the learning curve and provide the same user experience for customers looking to adopt this solution. The examples below show the familiar Device Health Monitoring dashboard, where you can find the overall health statistics of your deployment, and the Policy Editor from the cdFMC.
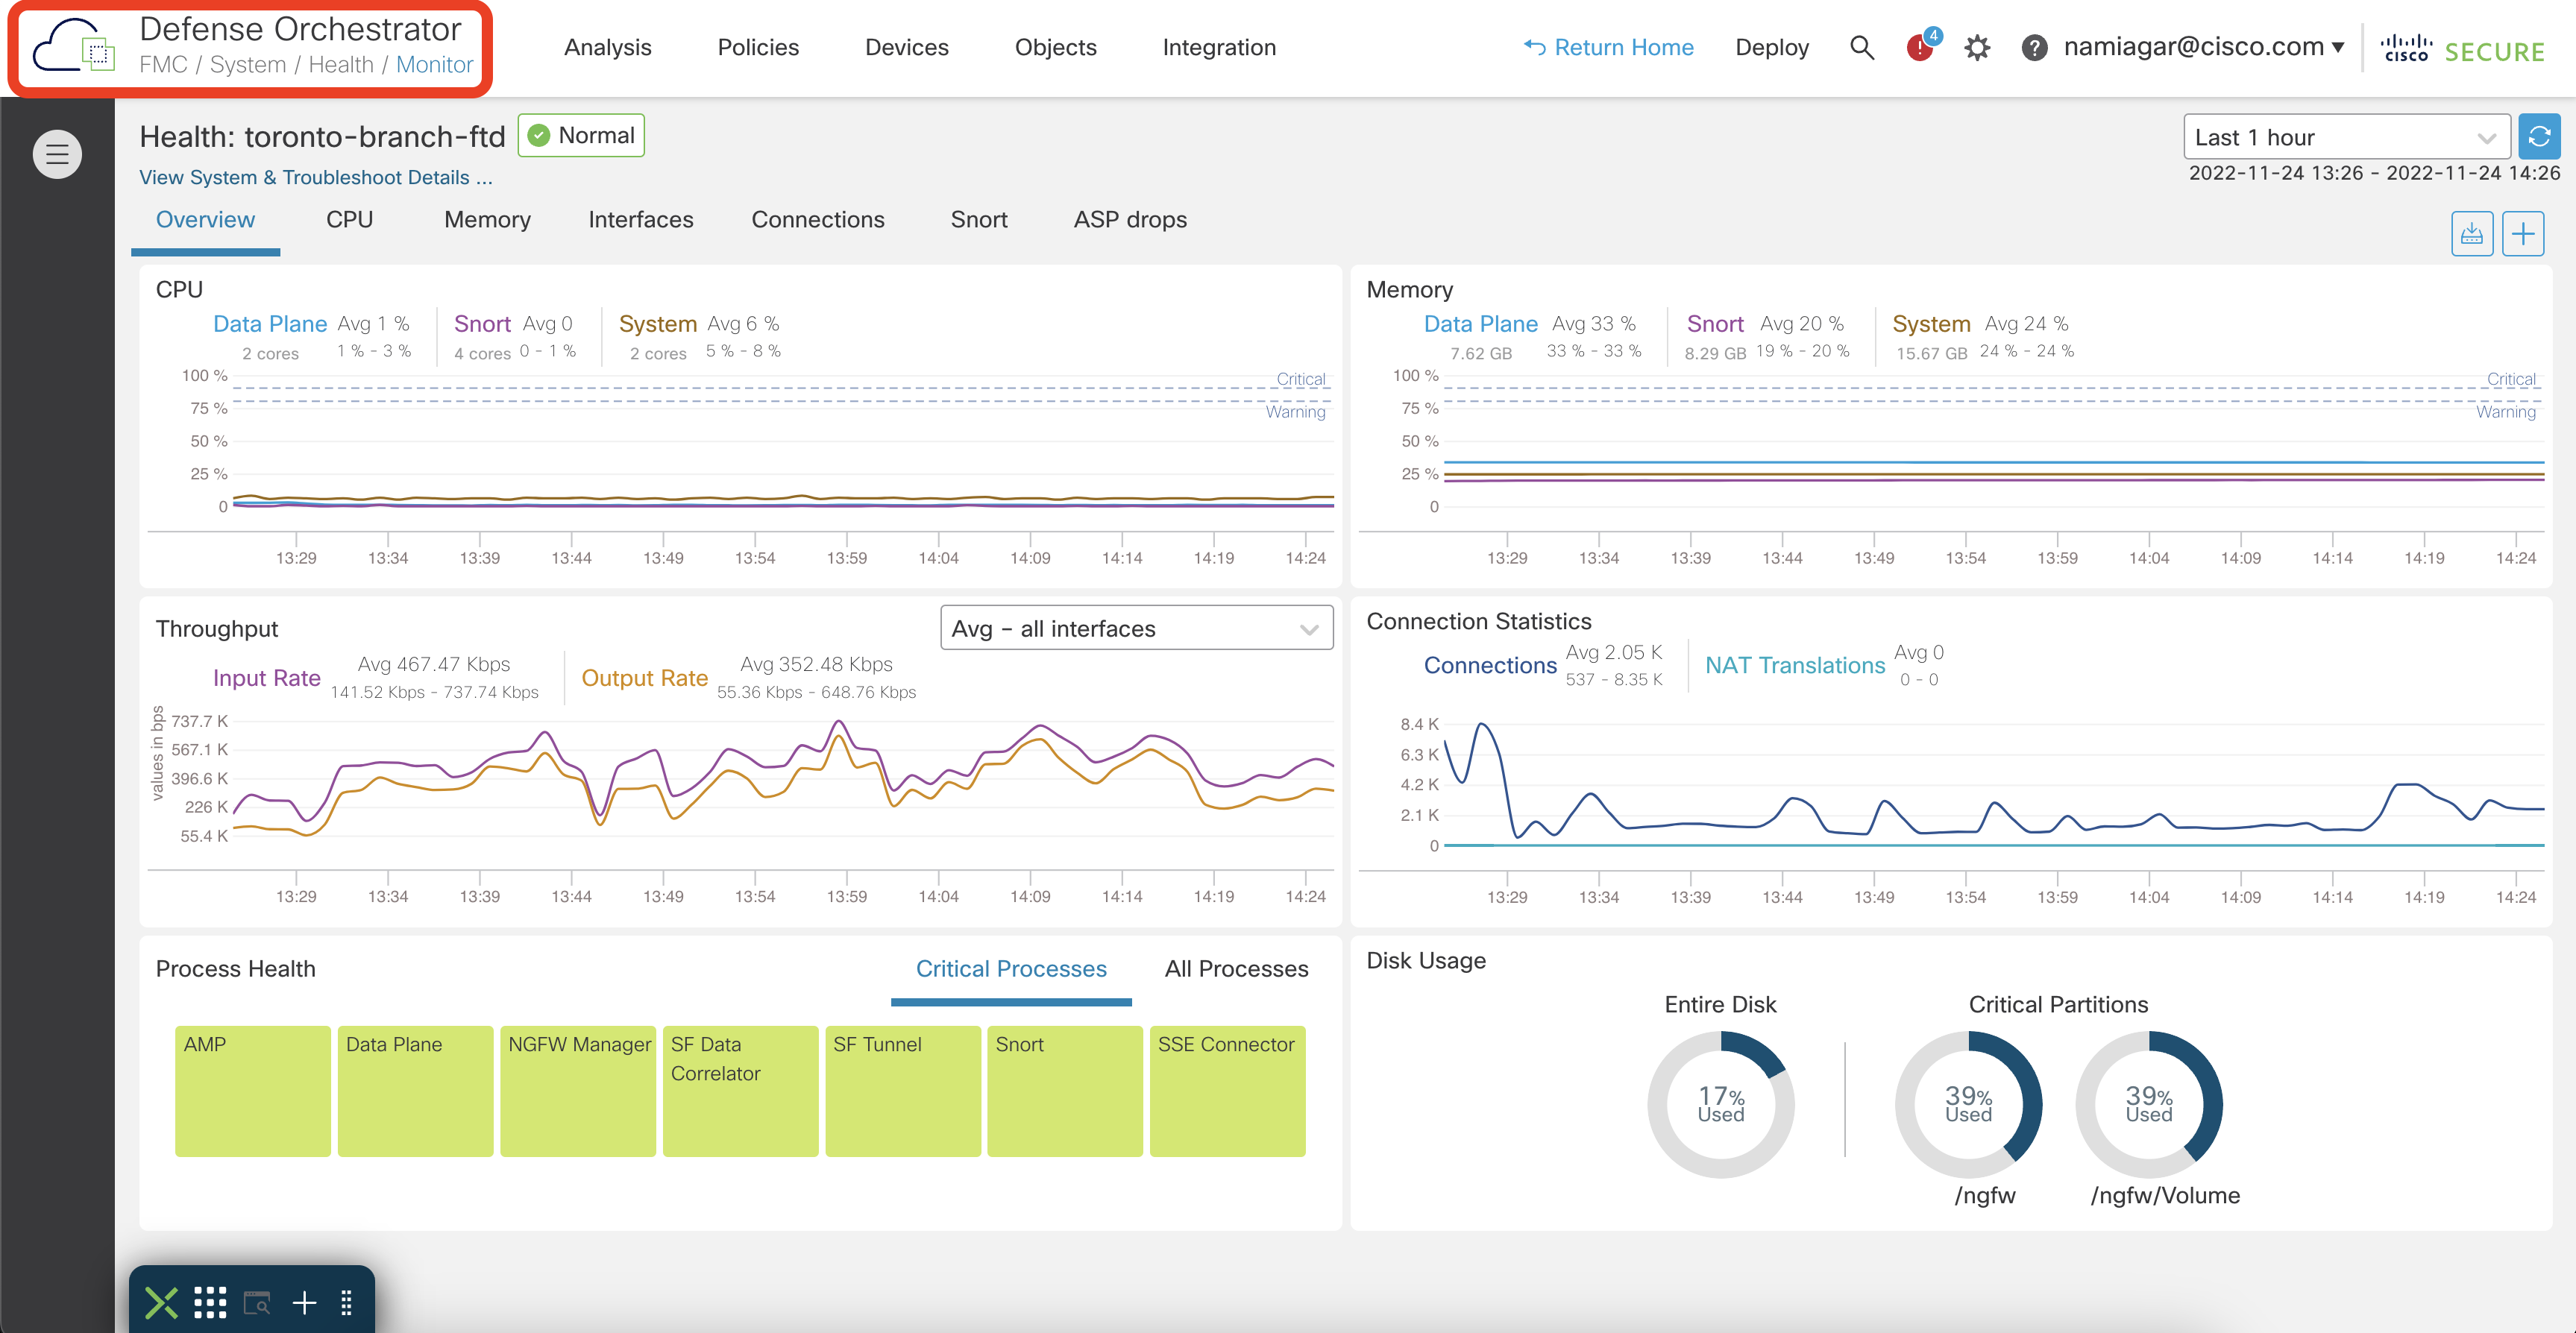
Device Health Monitoring Dashboard in cdFMC
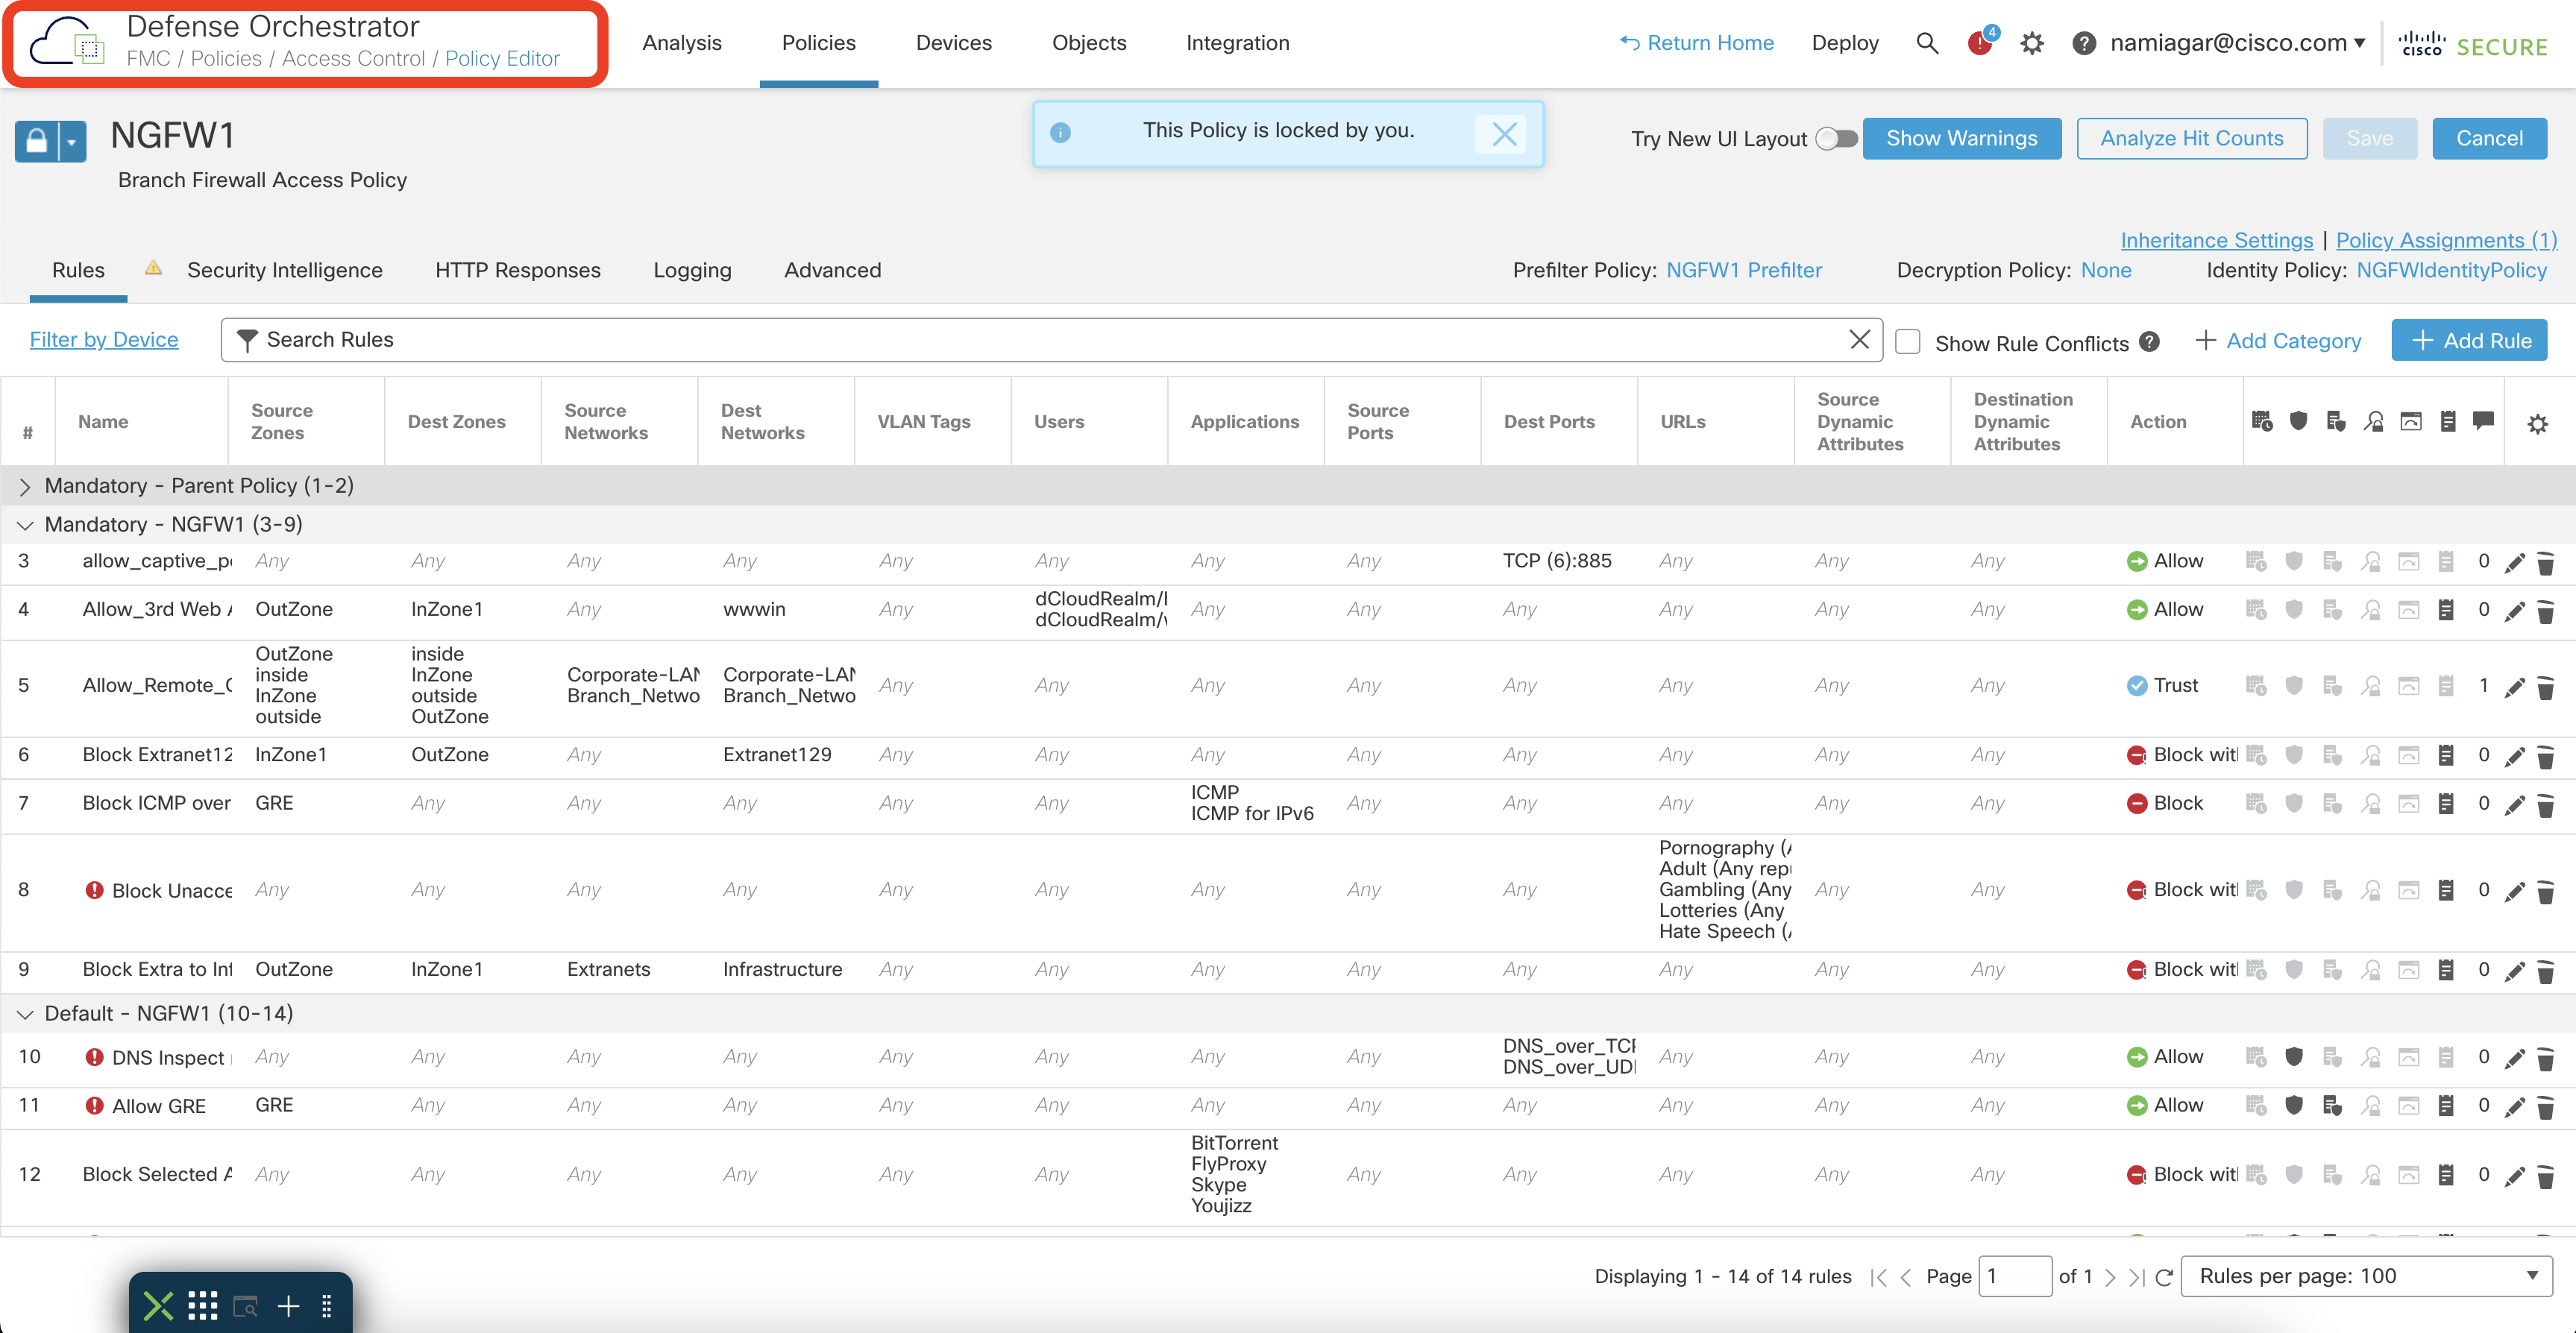
Access Policy Editor in cdFMC
Easy Onboarding and Migration Experience
The Device Onboarding and Migration workflows are driven through the Cisco Defense Orchestrator Home Page. A quick launch widget allows users to launch routine tasks with a single click.
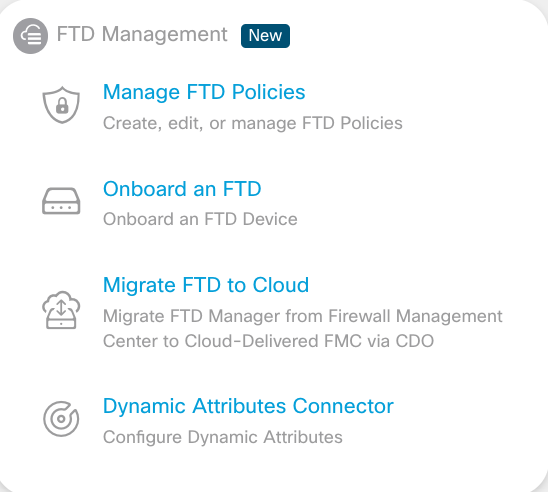
Quick Launch Widget on Cisco Defense Orchestrator (CDO) Home Page
The cloud-delivered FMC supports two onboarding methods:
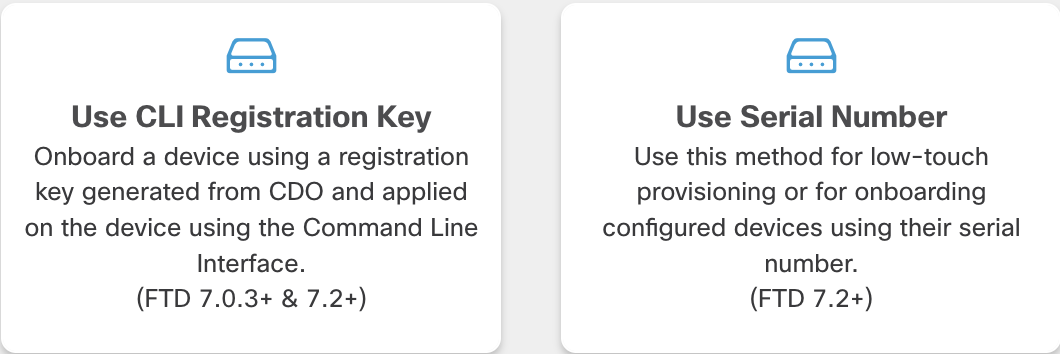
Onboarding Methods
Registration Key-Based Onboarding
The administrator generates a registration key from the Device Onboarding Wizard, which is then entered into the firewall using the CLI (similar to the FMC onboarding workflow).
Low Touch Provisioning
The administrator claims the Firewall by entering the firewall S/N into the Onboarding Wizard. Upon powering up and connecting to the Internet, the Firewall is automatically onboarded. This provides a low-effort onboarding experience, which is especially useful for provisioning remote branches. This method is limited to supported models and requires the documented factory-fresh installation state, software version, and cloud connectivity; check the current onboarding prerequisites before using it.
Migration from Privately Managed FMC
To move eligible Threat Defense devices from an on-premises FMC to cloud-delivered FMC, use the built-in Migrate FTD to Cloud-Delivered Firewall Management Center workflow. Onboarding an on-premises FMC to Security Cloud Control alone does not migrate its policies. Follow the prerequisites, compatibility checks, and analytics-destination choices in the current onboarding and migration documentation.
Migration from Other Firewalls
The Secure Firewall Migration Tool supports migration from ASA and 3rd party firewalls to Cisco Secure Firewall. Recently expanded to support migrations to cloud-delivered FMC as well. Now, the migration tool can migrate the firewall configuration to all deployments of the Firewall Management Center (on-premises, virtual, or cloud-delivered).
Simpler Branch Management
The introduction of the cloud-delivered FMC and recent firewall features makes branch provisioning very simple, enabling some key use cases around branch connectivity.
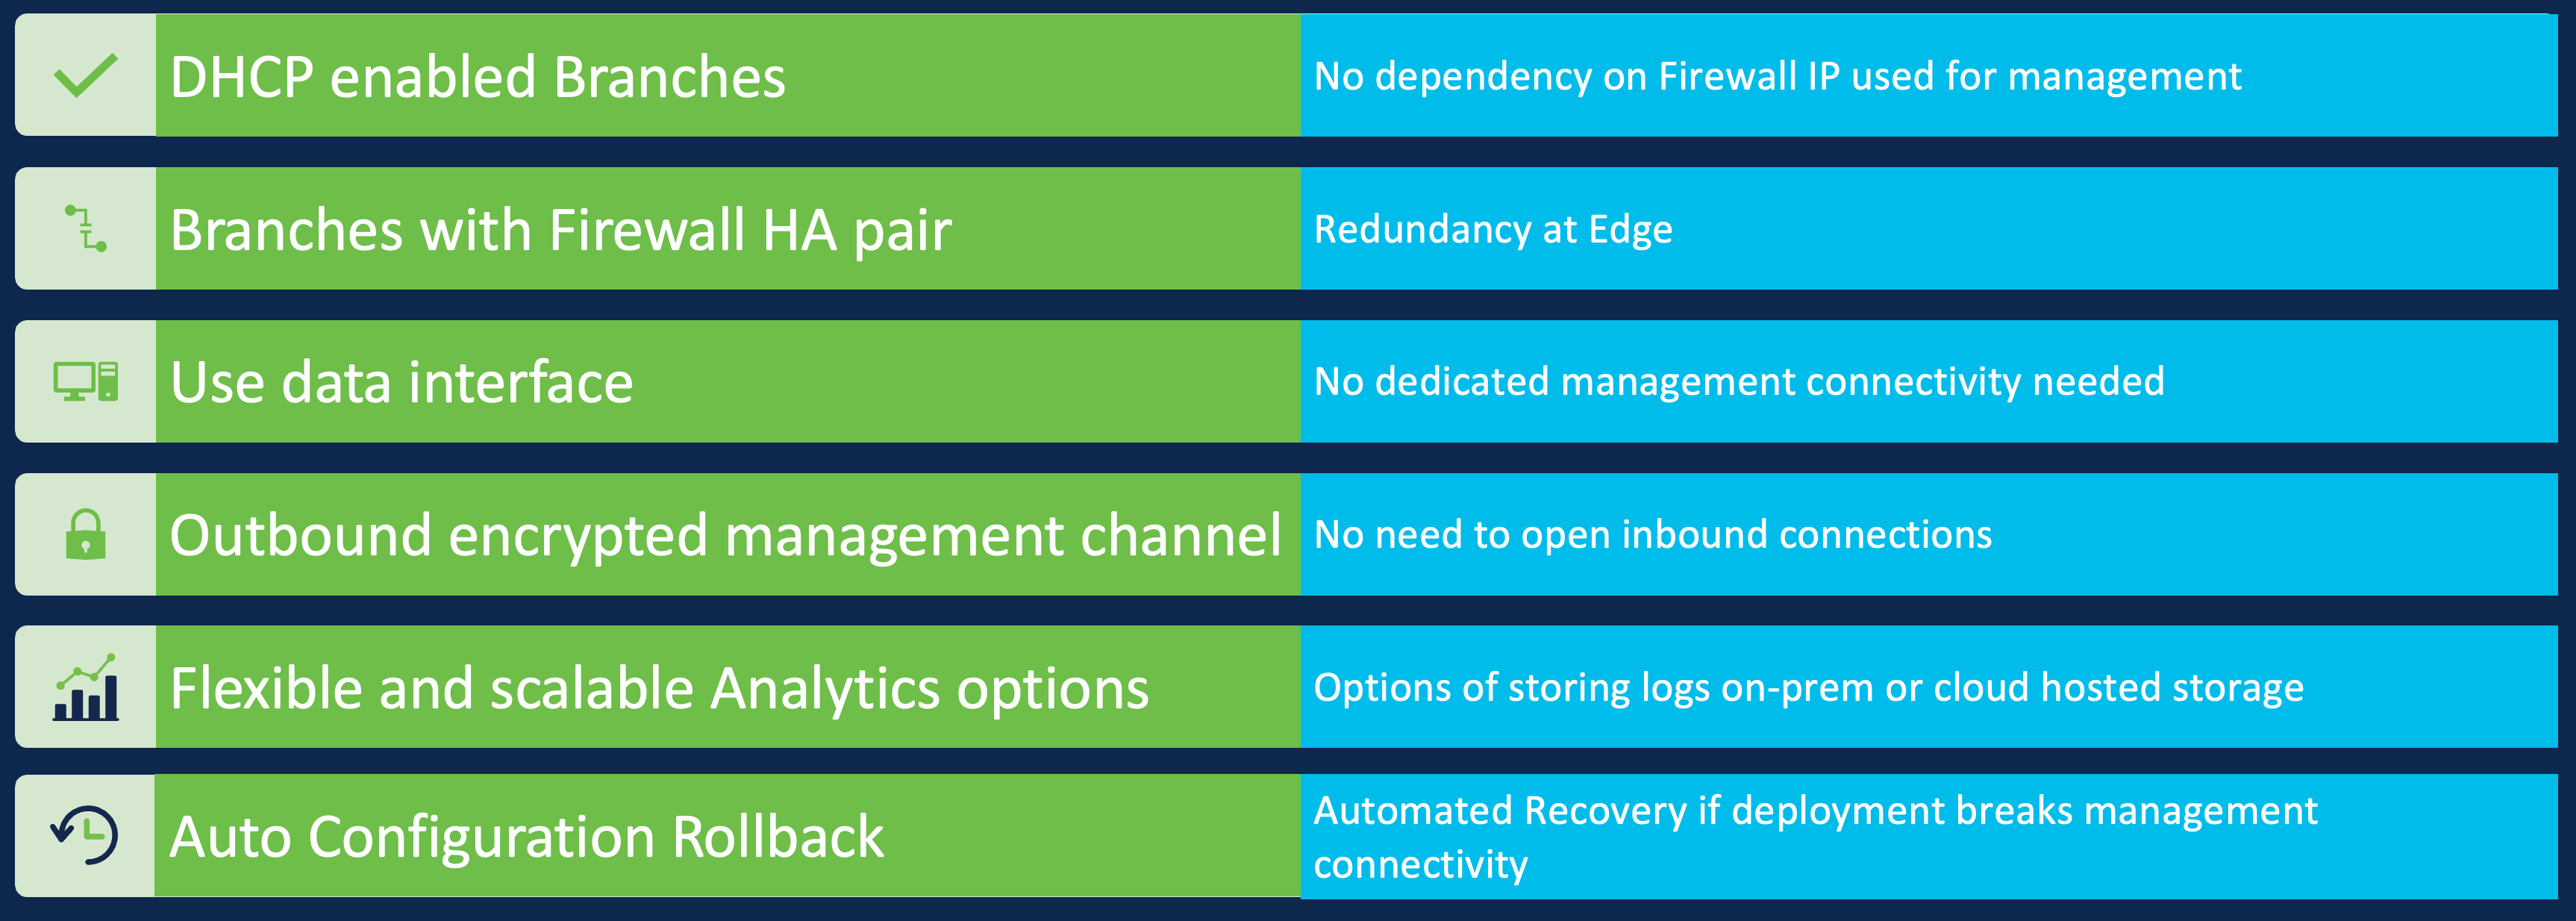
Easy Branch Management
Higher Scale of operations
The cloud-delivered FMC can manage up to 1000 firewalls per tenant. Also, to make the FMC components cloud compatible, we have added a lot of optimizations behind the scenes, allowing for a faster and lighter experience.
Cloud-hosted logging offers retention and capacity options according to the purchased entitlement. Check the applicable logging package and tenant requirements rather than assuming a single event-rate or retention limit for every deployment.
Because Cisco Defense Orchestrator is multi-tenant, the cloud-delivered FMC supports multi-tenancy where each tenant is completely isolated from the other, allowing for MSP deployments.
Easy Maintenance and Recovery
Cloud-delivered FMC is a Cisco-managed SaaS platform. Cisco handles infrastructure resiliency, platform recovery, and disaster recovery internally. The application interface does not offer a cloud-delivered FMC backup function; use Import/Export to retain supported policies, objects, templates, and settings externally. See About Backup and Restore. This description does not establish a 24-hour recovery-point guarantee for configuration or event data.
Support Multi-Cloud Scalable Adoption
The cloud-delivered FMC offers flexible deployment options depending on the use case requirements. For example, customers can manage the firewall from the cloud but retain the events with the sensitive information on-premises, or cloud-savvy customers can move the eventing and logging to the cloud with the unified event viewer in the cloud, offering both real-time and historical views.
- Complete Cloud Adoption - configuration management, log storage and analytics are cloud-delivered. It can be further enhanced by behavioural analysis from Secure Cloud Analytics (formerly Stealthwatch Cloud, as named in the original architecture). It can also send behavioural analysis alerts to an external SIEM.
- Logging to an on-premises FMC - configuration management is cloud-delivered, but the log storage and analytics are available through an on-premises FMC. It can be further enhanced by integrating with Cisco Security Analytics and Logging (On Premises), which provides additional behavioural analysis powered by Secure Network Analytics (formerly known as Stealthwatch Enterprise) or used to forward the logs to an external SIEM using eStreamer.
- External SIEM - You have the flexibility of logging into an external SIEM using any of the above options or directly sending syslogs from the Firewall.
NoteUsing the on-premises FMC for logging and analytics only requires running version 7.2 or later.
The Cisco Secure Firewall inherently supports granularity when choosing one or any of the above combinations for logging by providing the flexibility of choosing event types and their destination.
E.g., Connection Events can be streamed to the cloud, but the IPS and File and Malware events can be retained on-premises.
Dynamic Attributes Connector
Secure Firewall supports Dynamic Policies, allowing policy modification in near real-time, without any administrative action. 3rd Party and Cisco Secure products like ISE, APIC, and Secure Workload can integrate with the FMC and push policy updates in near real-time.
This is extremely critical for applications and workloads deployed in dynamic cloud environments. Cisco Secure Dynamic Attributes Connector aggregates attributes from the private, public cloud, and 3rd party feeds like O365 and uses them to update policies using the FMC APIs. It was introduced as a custom docker package, which could be installed on a dedicated VM. However, we have also made it available as a built-in component within CDO, eliminating the need to install and maintain a separate VM.
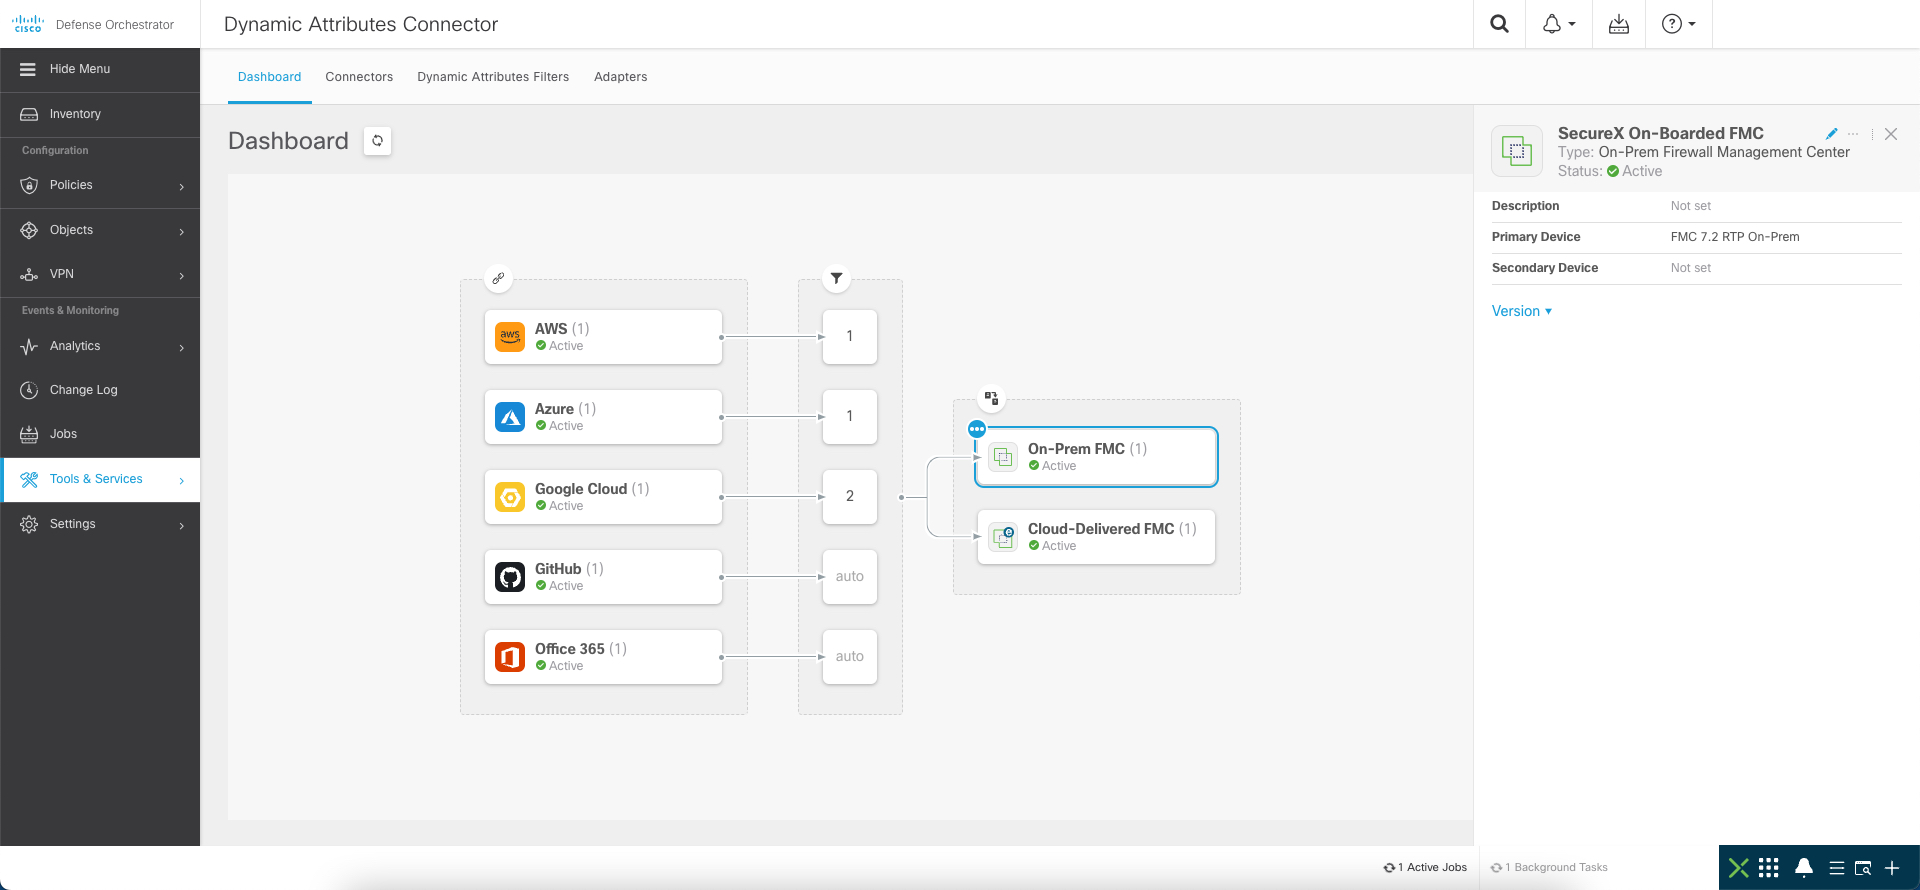
Cisco Secure Dynamic Attributes Connector in CDO
More details about the Cisco Secure Dynamic Attributes Connector are covered in depth here.
Licensing and Ordering Info
Cloud-delivered FMC is included in the Firewall Management offering in Security Cloud Control (formerly CDO). The licensing overview below follows the Security Cloud Control Firewall Management Ordering Guide (May 2026). Historical CDO ordering identifiers in older illustrations are not current ordering instructions.
- Base tenant and device management - Firewall management requires a base tenant subscription and per-device management entitlement. The device entitlement depends on the platform, not whether it runs ASA or FTD. Use the current ordering guide to select the applicable SKUs and deployment quantities.
- Cloud logging - Options include per-device management with unlimited logging and 90-day rolling retention, or separately purchased logging capacity. Standalone SAL tiers provide storage and retention choices; firewall-attached logging offers may use GB/day quantities. Select the offer that matches the deployment and consult its storage, ingest, and retention terms.
- Firewall feature licenses - Feature entitlements such as IPS, Malware Defense, and URL Filtering are separate from management and logging entitlements. Essentials and subscription requirements depend on the platform and applicable release. Confirm them in the corresponding licensing guide.
For current buying information, see the ordering guide.
Reference Docs
- cloud-delivered FMC Configuration Guide
- Firewall Migration Tool
- Cisco Defense Orchestrator Docs
- What's New in cloud-delivered FMC
Demo Resources
- Always-On Demo in dCloud (Cisco Internal and Partner access)
- Secure Firewall Youtube Channel
Updated 1 day ago